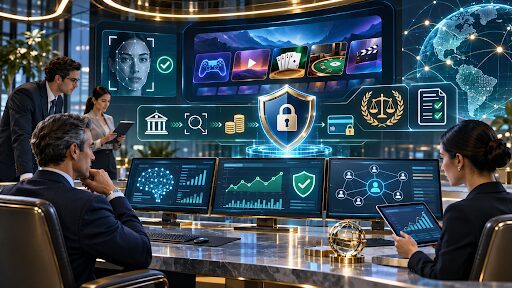
Digital entertainment depends on connected accounts, mobile devices, payment gateways, and international service providers. Leading platforms are combining anti-money laundering (AML) procedures with biometric identity checks, artificial intelligence (AI) and mature cybersecurity. For digital hospitality providers, the goal is to make these safeguards fit smoothly into the customer journey.
For US audiences, these controls help protect customers, payment partners and the wider financial ecosystem. Managing high-volume transactions requires enterprise-grade oversight. A well-governed high roller vip casino, for example, may use real-time AI monitoring, enhanced due diligence and audit trails alongside strict AML controls comparable in rigor to private banking and wealth management.
Regulatory Compliance Sets the Foundation
Regulatory compliance is central to responsible digital business operations. In the United States, the Bank Secrecy Act (BSA) establishes important requirements for covered financial institutions, including certain casinos and card clubs. FinCEN (Financial Crimes Enforcement Network) oversees relevant AML obligations, including suspicious activity reporting, recordkeeping and customer identification requirements.
The exact obligations depend on how a business is classified, its licensing arrangements and the jurisdictions in which it operates. Covered institutions must maintain appropriate compliance programmes, identify unusual financial activity and investigate transactions that may indicate money laundering or other financial crimes.
Internationally, the Financial Action Task Force (FATF) provides recommendations that guide countries in developing AML and counter-terrorist-financing frameworks. Its standards emphasise customer due diligence, transaction monitoring, beneficial ownership transparency and risk-based compliance.
Other regulatory frameworks also influence digital governance. The EU AI Act introduces requirements for transparency, accountability and risk management in certain AI applications. DORA (Digital Operational Resilience Act) strengthens ICT risk management and operational resilience for financial entities within its scope. Meanwhile, the EU’s Anti-Money Laundering Authority (AMLA) is developing a more coordinated approach to financial crime supervision across European markets.
Although these European regulations do not automatically apply to every US entertainment business, they demonstrate the growing importance of consistent governance across international digital services.
Biometric KYC Makes Digital Identity More Reliable
Know Your Customer (KYC) procedures help businesses establish customer identities before providing access to financial services. Traditional verification often involves government-issued identification, proof of address, and personal information. Next-generation platforms are expanding these checks through biometric technology.
Facial recognition, fingerprint verification and biometric liveness detection can strengthen digital identity checks. Liveness detection helps determine whether a verification attempt involves a real person rather than a photograph, prerecorded video or manipulated digital image.
These capabilities are particularly relevant as generative AI makes synthetic identities and deepfake content increasingly sophisticated. Combining document authentication with biometric checks, device intelligence and multi-factor authentication gives verification systems more information when assessing suspicious registration attempts.
Privacy remains equally important. GDPR and UK GDPR establish principles such as data minimisation, purpose limitation and appropriate information security for organisations within their scope. US businesses must also consider applicable federal and state privacy requirements, particularly when collecting biometric information.
The objective is to verify customers effectively without collecting unnecessary personal data. Clear privacy notices, controlled access, and appropriate retention policies help maintain customer confidence throughout the onboarding process.
AI Helps Detect Unusual Activity in Real Time
Artificial intelligence is changing how digital platforms monitor financial transactions. Instead of relying entirely on manual reviews, AI-powered systems can analyse large volumes of payment activity and identify patterns that require further investigation.
Real-time transaction monitoring can flag unusual deposits, repeated withdrawal attempts, unexpected payment changes and activity that differs significantly from an established customer profile. Behavioural biometrics and anomaly detection provide additional signals by examining device usage, login patterns and other account interactions.
Perpetual KYC (pKYC) takes this approach further by moving beyond one-time identity verification. Customer risk profiles can be reassessed as new information becomes available or transaction behaviour changes. Dynamic customer due diligence also supports ongoing sanctions and politically exposed persons (PEP) screening.
For higher-value transactions, source of funds (SoF) and source of wealth (SoW) verification can provide additional financial context. These checks help establish whether the funds involved are consistent with the customer’s declared financial circumstances and applicable risk requirements.
However, AI should support experienced compliance professionals rather than replace them. Human-in-the-loop (HITL) oversight allows trained analysts to examine alerts, assess supporting evidence and make appropriate escalation decisions.
Strong model governance is also essential. Platforms need to understand how their algorithms identify suspicious patterns, test for potential bias and document important decisions. The NIST AI Risk Management Framework provides a useful approach to evaluating AI reliability, transparency and accountability.
Cyber Governance Protects Payments and Customer Data
Effective AML programmes depend on reliable cybersecurity. Digital platforms process sensitive identity information and financial transactions, making information security an essential part of their operational responsibilities.
Zero-trust architecture (ZTA) is one approach to strengthening access controls. Rather than automatically trusting users or devices within a network, zero-trust systems continuously verify access based on identity, permissions and security conditions.
Encryption, tokenization and multi-factor authentication provide additional protection. End-to-end encryption helps protect information during communication, while payment tokenization replaces sensitive payment details with alternative identifiers. These technologies can reduce exposure when payment information is processed or stored.
Cryptographic verification and tamper-evident audit logs also support accountability. They help organisations maintain reliable records of important account activities, payment events and administrative decisions.
International security standards provide further guidance. ISO/IEC 27001 establishes a framework for managing information-security risks, while SOC 2 Type II assessments examine how service organisations maintain relevant security and operational controls over time.
Together, these practices help digital businesses strengthen their security programmes, manage third-party technology risks and maintain operational resilience.
Board Oversight Connects Security With ESG
AML and cybersecurity are not simply technical responsibilities. They are important elements of corporate governance and environmental, social and governance (ESG) performance.
The governance pillar focuses on accountability, transparency, risk management and responsible decision-making. Corporate boards can establish security priorities, approve compliance policies, review independent audit findings and ensure that internal teams have sufficient resources.
Model governance and algorithmic transparency also contribute to responsible oversight. Organisations should be able to explain how automated systems support financial monitoring and how human reviewers handle important decisions.
The social dimension is equally relevant. Customers benefit from accessible verification procedures, responsible information handling and fair account reviews. Employee training, independent security assessments and incident-response exercises help make these commitments part of everyday operations.
This approach supports fiduciary responsibilities and strengthens relationships with customers, payment partners and other stakeholders.
Building a More Accountable Digital Entertainment Ecosystem
Next-generation digital entertainment platforms are increasingly adopting practices associated with established financial services. Biometric identity verification, AI-powered monitoring, continuous customer due diligence and stronger cybersecurity are becoming important parts of modern operational governance.
For US businesses, effective implementation starts with understanding applicable federal and state requirements. International frameworks such as FATF recommendations, the NIST AI Risk Management Framework and ISO/IEC 27001 can provide additional guidance for strengthening internal controls.
Ultimately, technology works best when supported by experienced professionals, transparent policies and meaningful board oversight. By combining these elements, digital entertainment providers can protect customer information, strengthen financial integrity and contribute to a more secure and accountable digital ecosystem.